A comparison of NIS2 compliance options in Italy: spreadsheets, consultancy, international GRC platforms, Microsoft 365 security tools and Italian vertical tools such as Nispo. Selection criteria, costs and a comparison table.
“Which tool should I use for NIS2?” is the question that comes right after “does it apply to us?”. And the honest answer is: it depends on who you are. A 120-employee manufacturing SME and a bank don’t have the same problem, and they shouldn’t buy the same thing.
In this guide I line up the five options you really have in Italy in 2026, with their strengths, weaknesses, costs and how they combine. Full transparency up front: Nispo is our product. But the comparison is meant to help you choose, even if you end up choosing something else.
In short
- NIS2 compliance solutions fall into five categories: spreadsheets, consultancy, international GRC platforms, security tools such as Microsoft 365 and Italian vertical tools such as Nispo. They are not mutually exclusive: they are often combined.
- Security tools (Microsoft Defender, Intune, Entra ID) enforce technical controls; a compliance tool manages requirements, evidence, accountability, suppliers and reporting. These are two different jobs.
- For a medium-sized Italian company that only needs to manage NIS2, a vertical tool built on the ACN measures is usually the most efficient choice. For those managing several frameworks together, an international GRC platform.
What a NIS2 tool needs to do in Italy
Criteria first, names later. To be useful to an Italian essential or important entity, a tool has to:
- Cover the ACN controls, not just the text of the European directive. In Italy NIS2 is transposed by Legislative Decree 138/2024, and the actual controls are set by ACN’s basic security measures, which differ for essential and important entities.
- Check automatically what can be checked, by connecting to your real systems (e.g. Microsoft 365, Google Workspace, AWS, Google Cloud), and handle the rest with evidence linked to requirements.
- Collect the evidence continuously, because NIS2 requires compliance maintained over time, not a one-off stamp.
- Speak Italian, meaning the language but above all the regulations: ACN portal obligations, incident notification to CSIRT Italia, deadlines.
- Have an SME price tag, because the budget of an 80-employee important entity is not that of a multinational.
The five options on the table
1. Do-it-yourself with a spreadsheet
The starting point for almost every Italian SME: a sheet with the list of controls, a “status” column and plenty of goodwill.
- Pros: zero cost, total control, you can start right away.
- Cons: it is a snapshot that starts ageing the day after. No real control checks, evidence disconnected from requirements, no reminders, versions multiplying. NIS2 requires continuous compliance: a spreadsheet, by definition, isn’t.
- Makes sense if: you only want a very first internal gap analysis before deciding on a budget.
2. Traditional consultancy
The firm or consultancy that runs the assessment, writes the policies and prepares you for the audit.
- Pros: real regulatory expertise, support on organisational and legal aspects, judgement on complex cases.
- Cons: costs typically in five figures and output that is often documents describing the state at one moment. Without a tool, keeping evidence and tasks up to date over time falls to the company.
- Makes sense if: you have a complex organisational situation (groups, multiple sites, disputes) or no in-house expertise at all. Combines well with a tool.
3. International GRC platforms
The compliance platforms born for SOC 2 and ISO 27001 — names like Vanta, Drata, OneTrust — which have added NIS2 to their framework catalogue.
- Pros: mature automation, lots of integrations, great if you need to manage several frameworks together (ISO 27001 + SOC 2 + NIS2).
- Cons: NIS2 is one framework among many. Check whether the catalogue covers the Italian transposition and the ACN measures or only the EU directive text, whether the interface and support are available in Italian and whether the price suits an SME.
- Makes sense if: you are an already structured company, perhaps with foreign customers asking for SOC 2, and NIS2 is just one of your obligations.
4. Microsoft 365 security tools
Depending on the plan, Microsoft 365 Business Premium and E3/E5 include Microsoft Entra ID (MFA, conditional access), Intune (device management and compliance), Microsoft Defender (endpoint and email protection) and Microsoft Purview (data protection; Compliance Manager offers assessment templates, including one for the NIS2 Directive, focused on the Microsoft environment).
- Pros: they actually enforce many technical controls required by the ACN measures, and they are often already licensed.
- Cons: their scope is the Microsoft environment. They do not keep a supplier register, manage the approval of policies by management or handle administrative documentation structured on the ACN measures.
- Makes sense if: you use Microsoft 365, which is almost always. Not an alternative to a compliance tool, but the technical foundation it builds on. Who does what, in detail: Nispo and Microsoft 365.
5. Italian vertical tools: Nispo
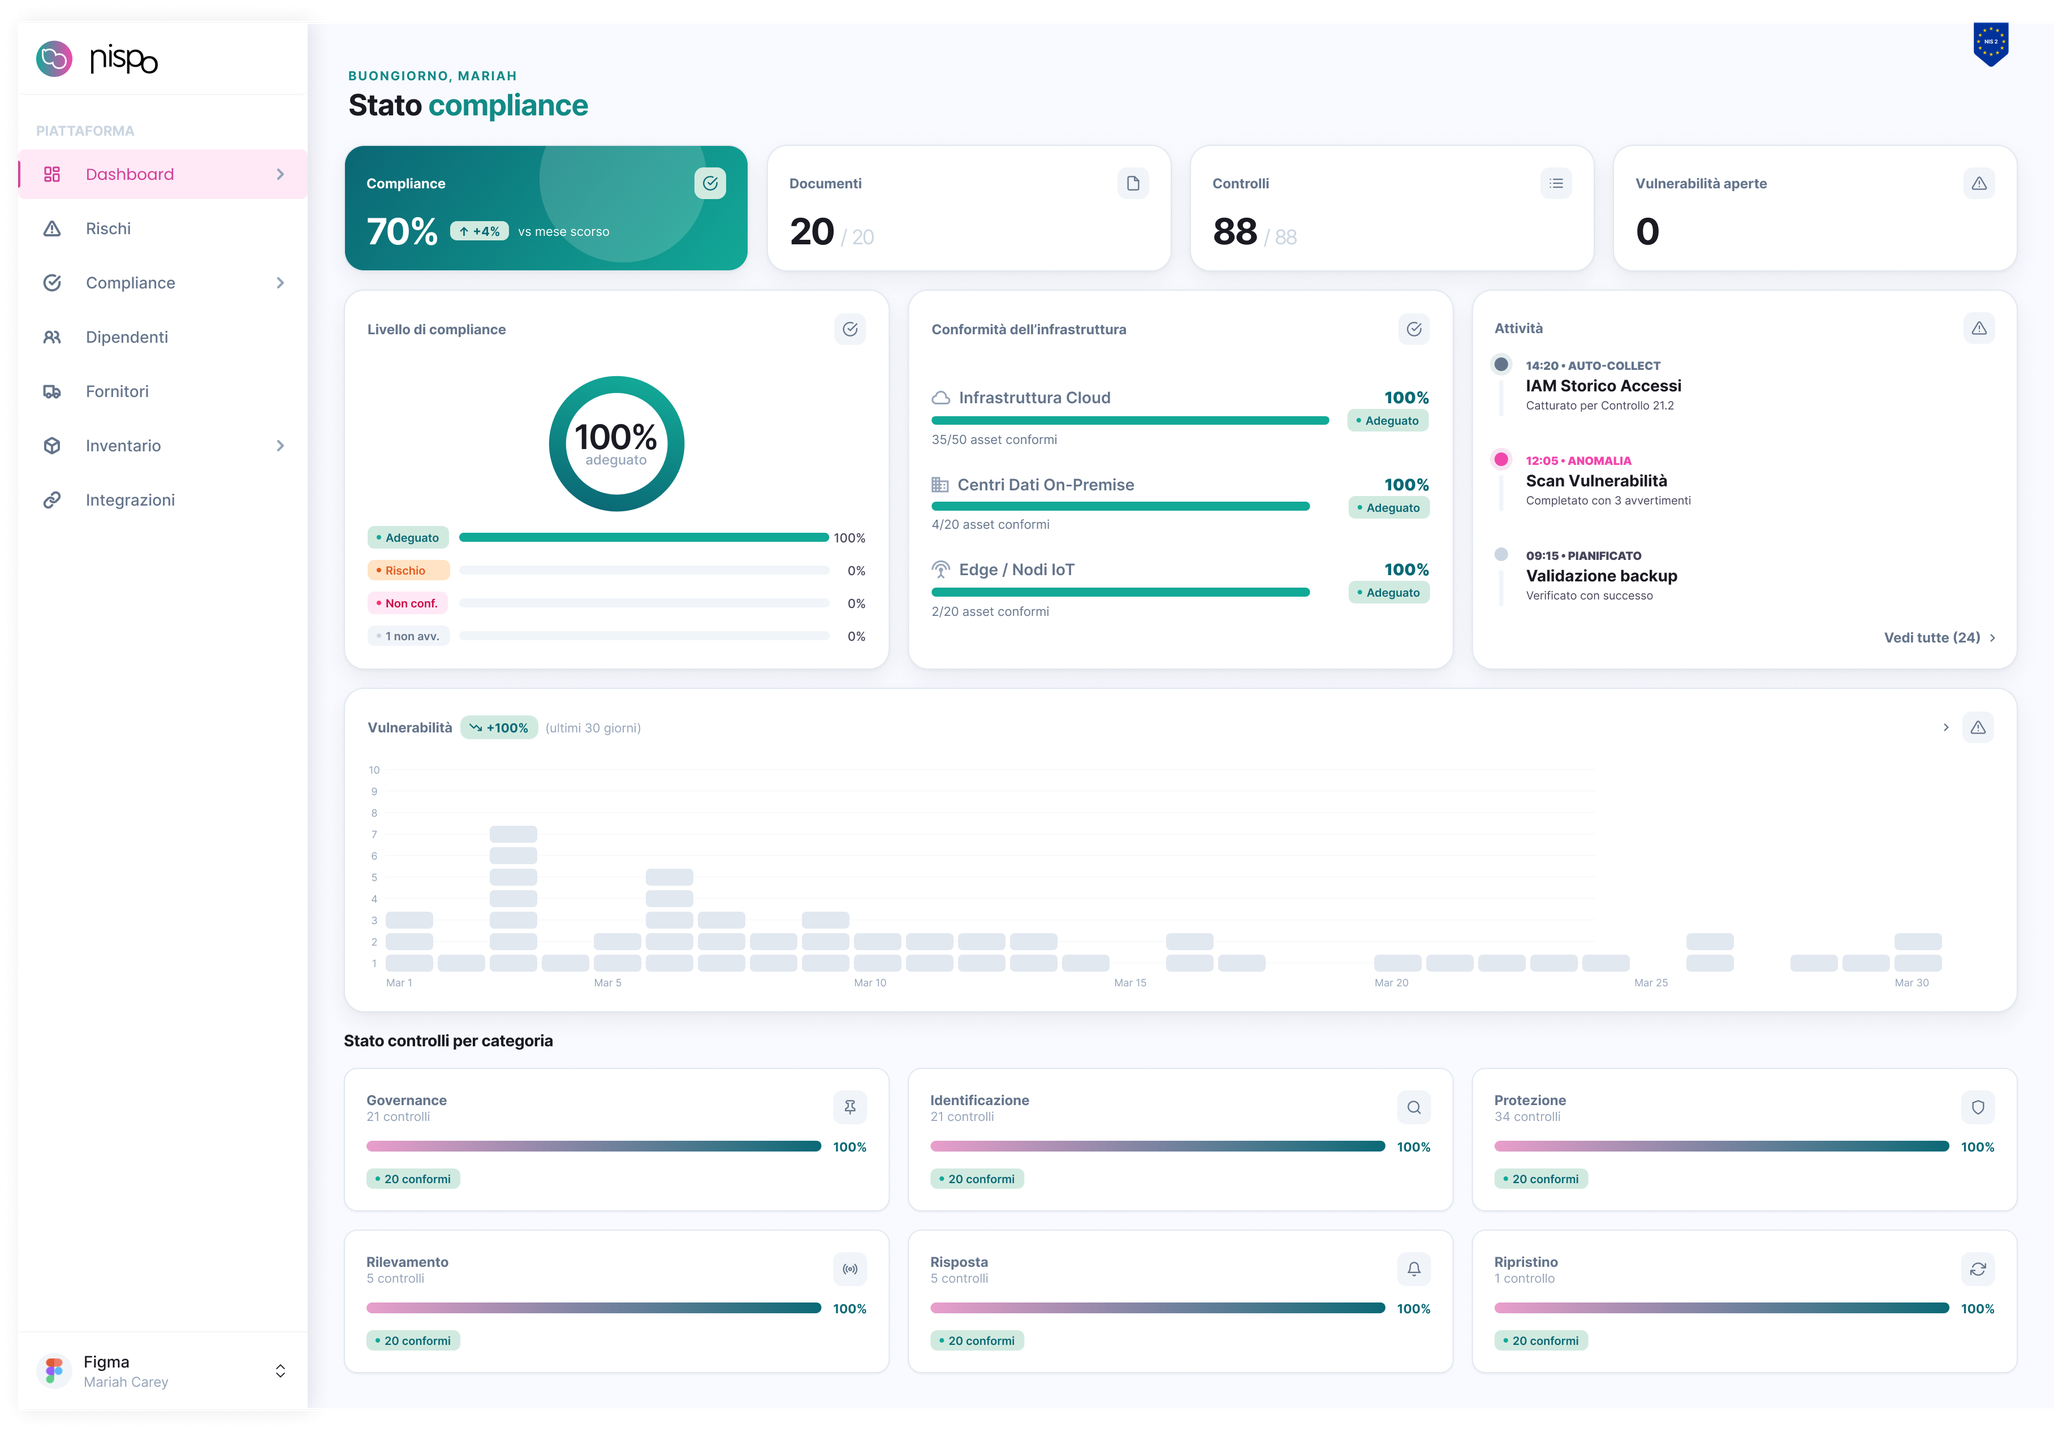
The opposite approach to international platforms: a tool built only for Italian NIS2. This is the category Nispo belongs to, designed for Italian organisations classified as essential or important entities, starting from 50 employees and 20 IT assets.
How it works in practice:
- You connect your systems: Microsoft 365 (read-only, no changes to your configurations), Google Workspace, AWS or Google Cloud. Platform data is hosted in the EU.
- Nispo organises requirements in a control register structured on the ACN basic security measures and automatically checks the technical ones linked to the integrated systems (for example admin MFA); the others are handled with your team’s evidence and approvals.
- Every piece of evidence, automated or uploaded, is linked to its requirement with date, source and owner, and can be exported for inspectors.
- From the inventory and the supplier register it generates the files for the ACN portal: categorisation of activities and services and the list of relevant NIS suppliers.
- For the organisational side there are policy and plan templates to adapt and, if you need ongoing coverage, the vCISO service on quote. If you also buy penetration testing or vulnerability assessment, the findings become remediation tasks in the register.
- Pros: ACN controls already mapped, ACN portal files, everything in Italian, continuous compliance instead of one-off assessments, pricing designed for mid-sized companies, presented in a demo.
- Cons: it is vertical by design: if you also need to cover DORA or SOC 2 on the same platform, it isn’t the right tool. And automation covers Microsoft 365, Google Workspace, AWS and Google Cloud: for other systems (on-premise servers, network devices) evidence is uploaded by hand.
Comparison table
| Criterion | Spreadsheet | Consultancy | International GRC | Microsoft 365 | Nispo |
|---|---|---|---|---|---|
| Main purpose | Manual list | Expertise and guidance | Manage several frameworks | Enforce technical controls | Manage Italian NIS2 compliance |
| ACN controls already mapped | ❌ | ✅ (manual) | ⚠️ to be checked | ❌ | ✅ |
| Enforces technical controls (MFA, EDR, devices) | ❌ | ❌ | ❌ | ✅ | ❌ |
| Automated control checks | ❌ | ❌ | ✅ depending on integrations | ✅ on its own environment | ✅ Microsoft 365, Google, AWS |
| Evidence linked to requirements | Manual | In delivered documents | ✅ | Partial | ✅ |
| Supplier register | Manual | One-off | Often yes | ❌ | ✅ |
| Remediation with owners and due dates | Manual | In the delivered plan | ✅ | For Microsoft actions | ✅ |
| ACN portal files | ❌ | Manual | ⚠️ to be checked | ❌ | ✅ |
| Board reporting | Manual | ✅ periodic | ✅ | ❌ | ✅ |
| Italian language and regulatory context | ✅ | ✅ | ⚠️ to be checked | Partial | ✅ |
| CISO support | ❌ | ✅ (billed) | ⚠️ to be checked | ❌ | vCISO on quote |
| Cost for an SME | € | €€€€ | €€€ | Often already licensed | €€ (price in a demo) |
| Multi-framework (ISO, SOC 2, DORA) | ❌ | ✅ | ✅ | ❌ | ❌ (NIS2 only) |
How they combine
- Microsoft 365 + Nispo. Microsoft enforces the technical controls, Nispo checks their status, manages the rest of the requirements and produces the documentation.
- Consultant + Nispo. The consultant guides the choices, Nispo keeps the register, evidence and tasks over time.
- International GRC + Microsoft 365. For groups with several frameworks and a structured compliance team.
How to choose in 30 seconds
- You only need to know where you stand → start with a gap analysis, even on a spreadsheet, but give yourself a deadline.
- You are a structured group with several frameworks to manage → look at the international GRC platforms and budget for the ACN mapping.
- Your organisational situation is complicated → traditional consultancy first, a tool afterwards.
- You lack the basic technical controls → configure your security tools first (Microsoft or equivalent): no compliance tool replaces them.
- You are an Italian SME, an essential or important entity, on Microsoft 365, Google Workspace, AWS or Google Cloud → a vertical tool like Nispo gives you the ACN control register, automated checks on your systems, evidence linked to requirements, the ACN portal files and NIS2 templates ready to adapt.
If you want to see in practice the difference between a questionnaire and a real control check, book a 30-minute demo: we connect your tenant and you look at your own data, not slides.
- What is the best NIS2 compliance software in Italy?
- Do international GRC platforms cover Italian NIS2?
- Is a spreadsheet enough for NIS2 compliance?
- How much does a NIS2 compliance tool cost?
- I have Microsoft 365 Business Premium or E5: do I need a NIS2 tool?
- Does Nispo replace a cybersecurity consultant?