ACN controls mapped
A control register structured on the ACN basic security measures, with code, area, owner and status for each requirement.
Platform and features →Nispo · NIS2 Compliance Management Platform
Manage NIS2 controls, evidence, suppliers and remediation in one platform. Designed for organisations operating under the Italian NIS2 framework: Legislative Decree 138/2024 and the ACN basic security measures.
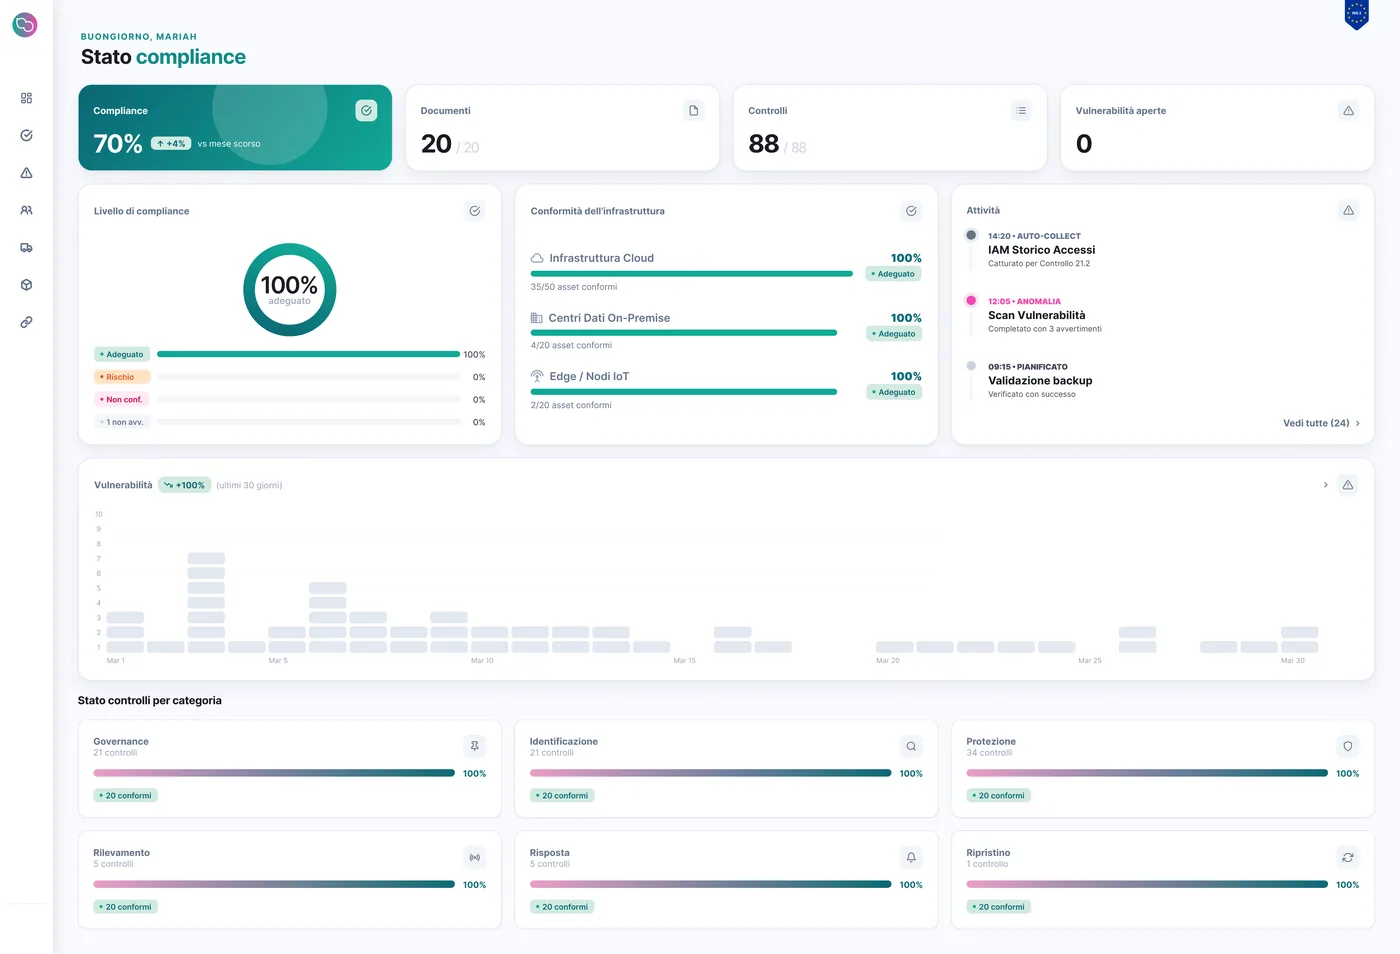
Real platform screen, with demo data
What it does
A control register structured on the ACN basic security measures, with code, area, owner and status for each requirement.
Platform and features →Every piece of proof with date, source and owner. Checks on Microsoft 365, Google Workspace, AWS and Google Cloud record their result automatically.
Evidence management →Gaps ranked by priority; each one becomes a task with an owner, a due date and closure verification.
NIS2 gap assessment →Versioned, approved policy templates; a supplier register with criticality, questionnaires and deadlines.
Suppliers and supply chain →Dashboard by area, reports for the management body and PDF and CSV exports for inspectors.
NIS2 compliance reporting →The problem
The ACN measures require documentation that is updated whenever something changes and easily accessible, plus verified technical controls. With checklists, shared folders and one-off tests, every inspection starts from scratch.
Five sources of friction we find in almost every company at the first assessment.
Screenshots, exports and minutes spread across inboxes and shared folders. Nobody knows which version is the right one.
A gap analysis describes the state of a single day. System configurations change every week.
Supply chain security is mandatory, yet questionnaires sit in email attachments with no deadlines or outcomes.
Management bodies approve the measures and are liable for them. Without a register, proving due diligence takes weeks.
An approved policy doesn’t tell you whether an attacker can get in. Without technical testing, measures stay on paper.
Deadlines towards CSIRT Italia from the moment you become aware of the incident; the final report within one month.
How it works
Nispo automatically checks what it can read from the integrated systems — Microsoft 365, Google Workspace, AWS, Google Cloud — and organises everything else: requirements, documents, suppliers and tasks. Where a hands-on check is needed, our specialists step in.
Set your category (important or essential), scope and owners. The control register follows the ACN basic security measures.
Connect Microsoft 365, Google Workspace, AWS or Google Cloud for automated checks; for everything else, upload documents and evidence starting from the templates.
Gaps become tasks with an owner and a due date. Where needed, penetration tests and vulnerability assessments check how effective the fixes are.
Dashboard, board reports and exports for inspections, updated with every new check, document or task.
↻ The cycle starts again whenever your systems, suppliers or ACN rules change. The full workflow, step by step →
Integrations
Nispo connects to Microsoft 365 / Entra ID read-only and integrates with Google Workspace, AWS and Google Cloud: control checks and the inventory update on their own. CSIRT Italia bulletins arrive in the platform.
For other systems, such as on-premise servers and network devices, controls are handled with uploaded evidence. What each integration checks →
Nispo and Microsoft 365
With Microsoft 365 Business Premium or E3/E5 you already have tools that implement many technical requirements. Nispo does not replace them: it uses them as a source of evidence and manages the rest.
NIS2 in Italy
In Italy the concrete requirements are those of Legislative Decree 138/2024 and the ACN determinations. Nispo starts from there.
Who it is for
Services
When the platform finds a gap, our specialists help you verify it and close it. The results flow back into the register as actions and audit evidence.
NIS2 requires you to assess how effective your security measures are. A penetration test does that in the most direct way: our specialists try to break in, as an attacker would, and document what works and why.
| Finding | Severity | In the register |
|---|---|---|
| Admin panel exposed with default credentialsExternal perimeter | Critical | In remediation · M. Ferri |
| SMB signing not required on file serversInternal network | High | Assigned · IT |
| Service account with Domain Admin privilegesActive Directory | High | Assigned · IT |
| TLS 1.0 enabled on the customer portalExternal perimeter | Medium | Closed · retest passed |
| User enumeration on the VPNExternal perimeter | Medium | Scheduled |
Tests that measure how well systems, network and identities hold up against a real attack.
Phishing and training with results that count as evidence.
Incident readiness and business continuity, tested in practice.
A dedicated CISO, without hiring one full time.
Services are also available without the platform. Request an assessment → All services →
A 30-minute demo on your Microsoft 365 tenant: we show you your real controls, evidence and gaps, and where to start.